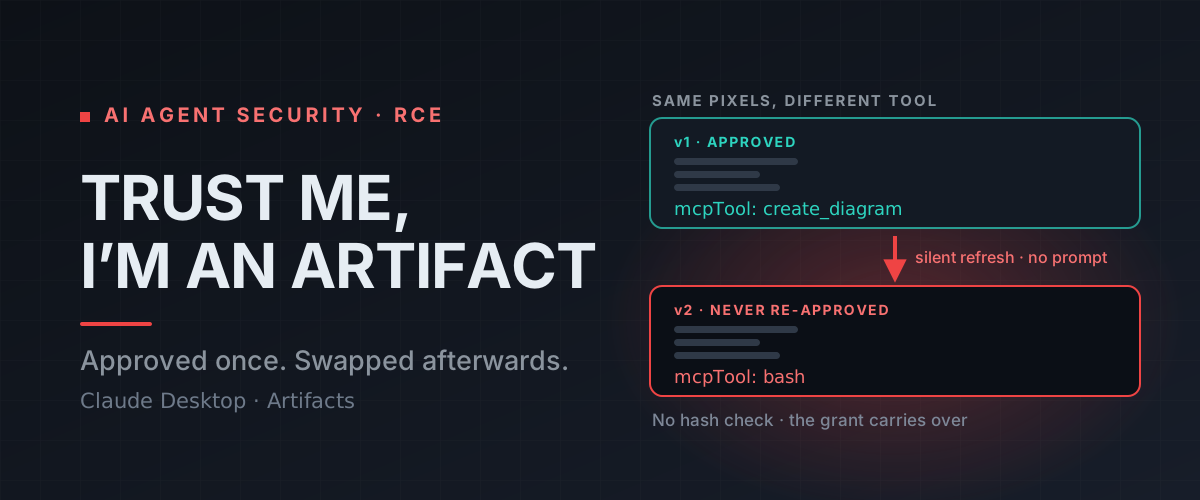
Trust Me, I'm an Artifact: I'll Just Borrow Your Shell
Originally published on Bloom Security.
Research
Deep dives into real-world security research, IoT hacking, and attack chain analysis.
Trust Me, I'm an Artifact: I'll Just Borrow Your Shell
Originally published on Bloom Security.
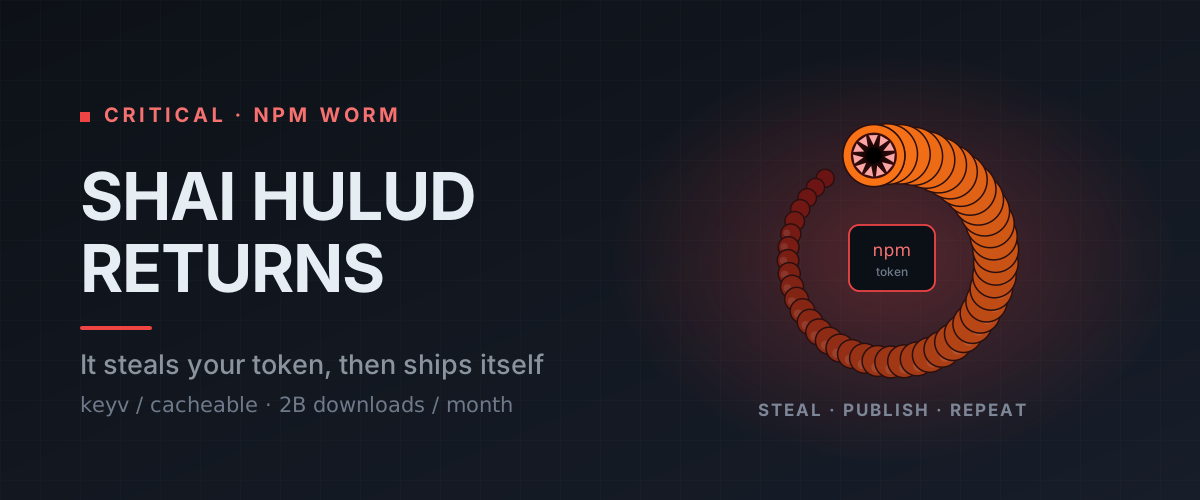
Shai Hulud Returns: Keyv and the Caching Ecosystem Hit in a Self-Replicating NPM Attack
Originally published on Bloom Security.
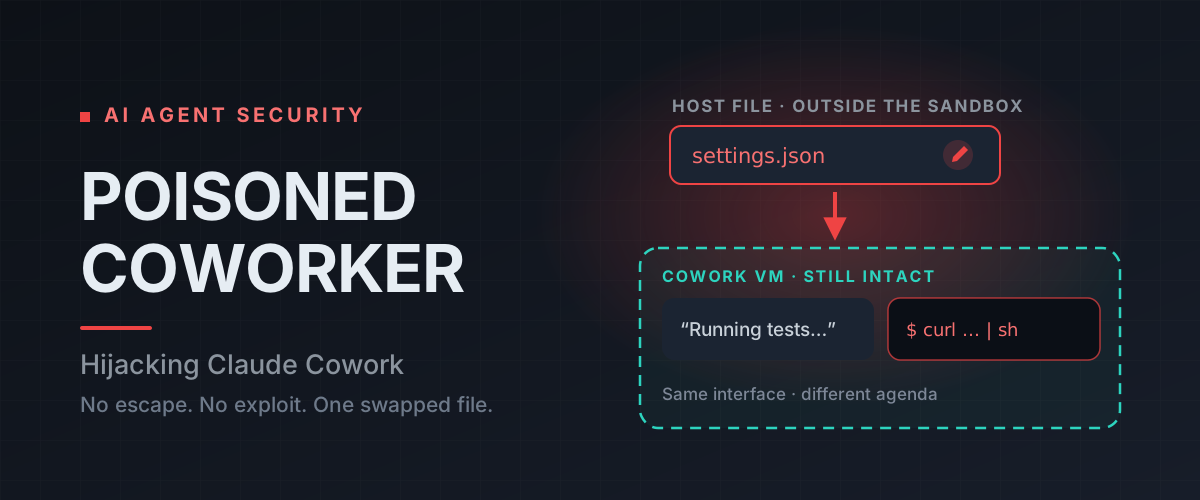
Poisoned Coworker: Hijacking Claude Cowork
Claude Cowork is sold as a safe place to do dangerous things: an AI coworker that lives inside a real Linux VM...
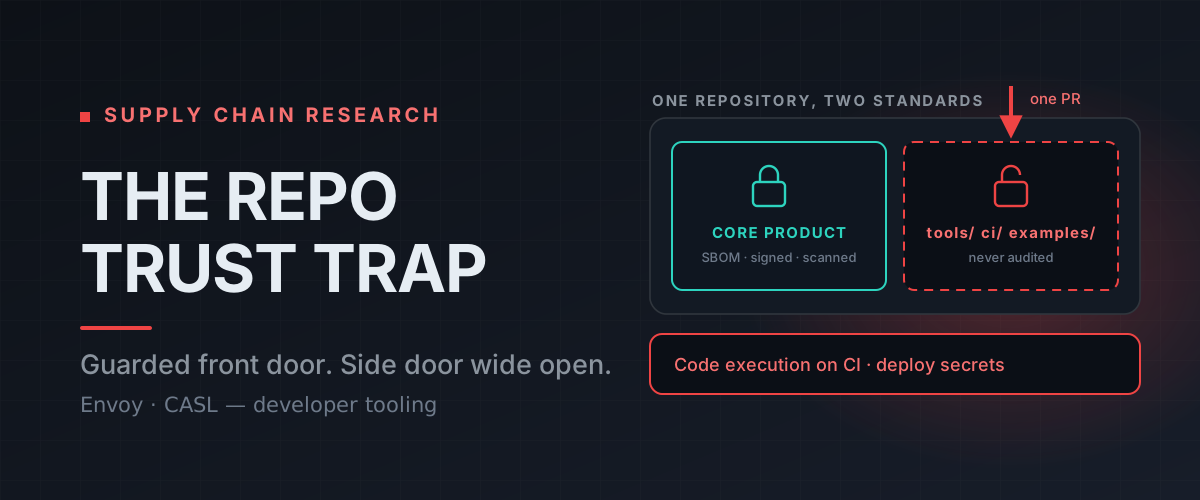
Securing the Core, Ignoring the Door: The Repo Trust Trap
TL;DR I found OS Command Injection (CWE-78) in the developer tooling of two widely-used open-source projects: Envoy (CNCF graduated, powers Istio) and...
Recent Advisories
The six newest disclosures. The full index is filterable by severity, vendor and year.
Tab Hijacking in Todoist for Chrome: One postMessage to Anywhere
Todoist for Chrome is the official browser extension from Doist for the Todoist task manager, with over 3 million users on the...
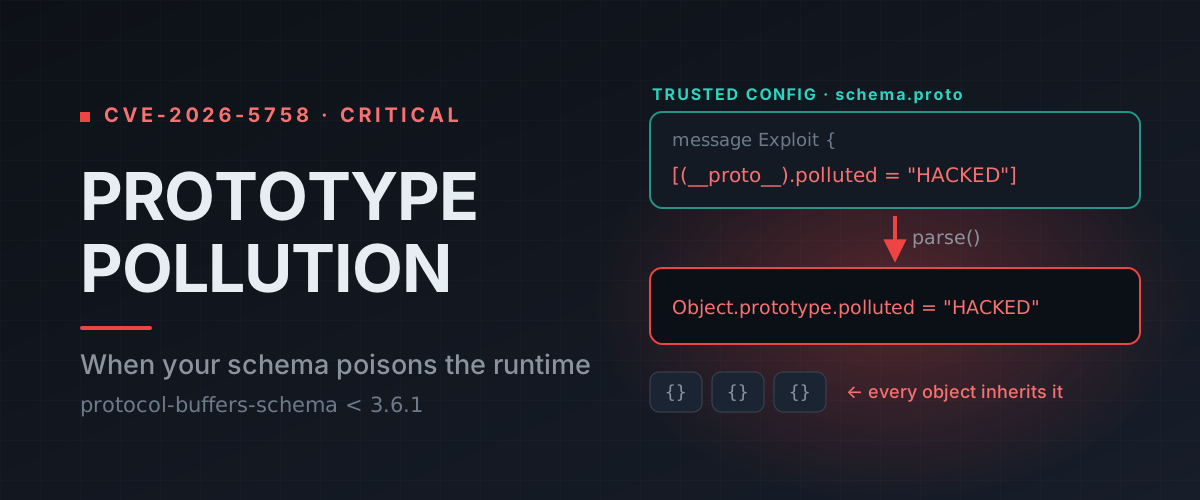
Prototype Pollution via .proto: When Your Schema Poisons the Runtime
protocol-buffers-schema is an npm package for parsing Protocol Buffer schema definitions. It is the schema parser behind protocol-buffers, one of the original...
Replican't: When Deserialization Starts Writing Your Script
replicator is an npm package for advanced JavaScript serialization and deserialization. It extends regular JSON behavior and lets applications encode and restore...
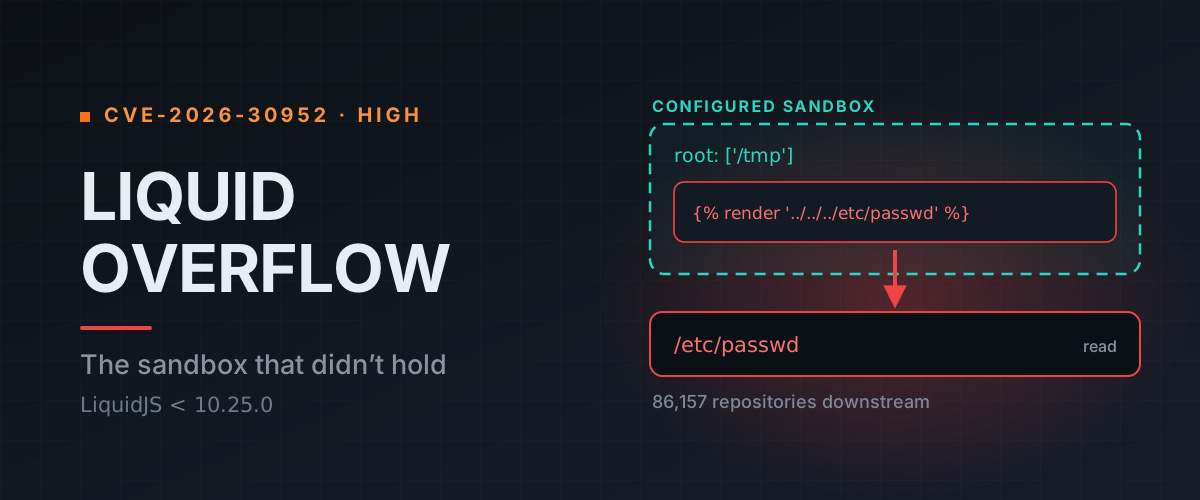
LiquidOverflow — How a Template Engine Exposed 86,000 Repositories to Arbitrary File Read
Templating engines are the silent workhorses of the web. They sit between your data and your users, quietly rendering pages, emails, and...
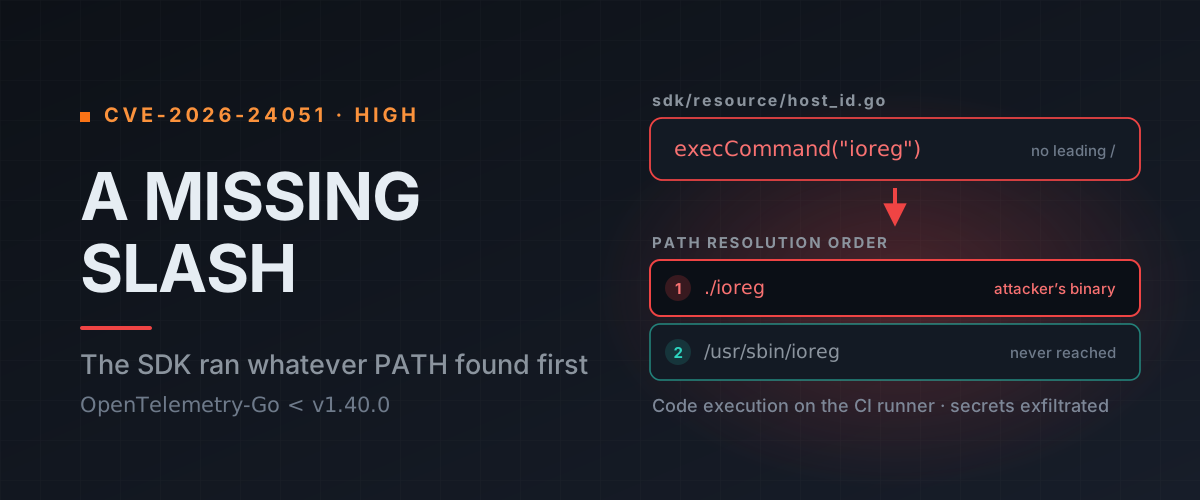
i0Regret: Breaking the Chain — How a Missing Slash Led to Arbitrary Code Execution
In the cloud-native ecosystem, we rely on SDKs as the “truth” for telemetry and observability. We assume these libraries are passive observers,...
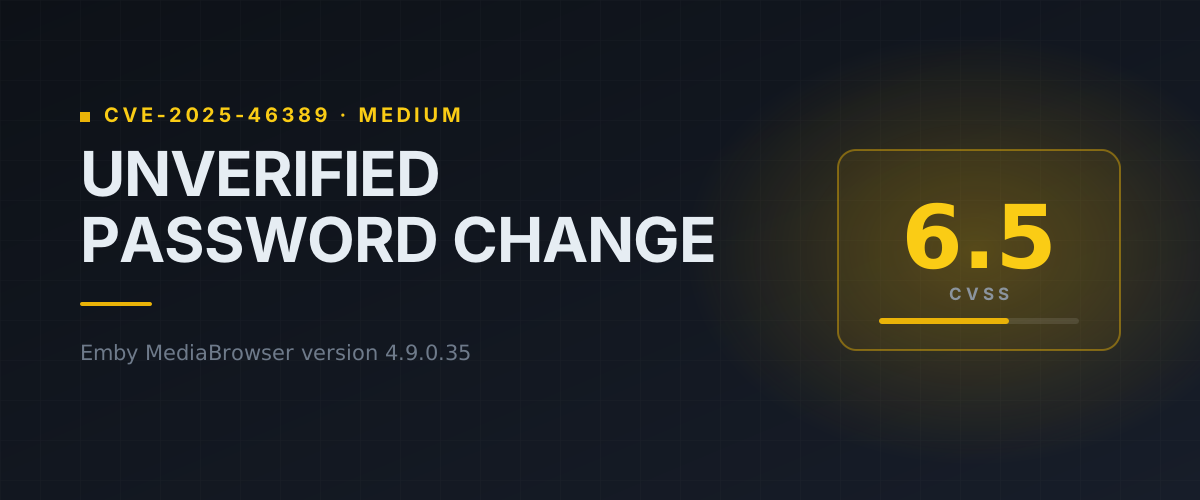
Unverified Password Change
Emby is a popular self-hosted media server platform used to organize, stream, and share personal media libraries across devices. It handles user...